

Securing Oracle Database Compliance in Air-Gapped Environments
In highly secure sectors—such as finance, healthcare, defense, and critical infrastructure—air-gapped networks are standard. These environments are completely isolated from the public internet to protect sensitive data from cyber threats.
However, security isolation creates a significant operational challenge: Software Asset Management (SAM).
Traditional SAM tools rely on constant cloud connectivity to send discovery payloads, download signature updates, and report compliance metrics. In an air-gapped system, these tools fail completely.
Here is how you can maintain absolute Oracle Database license compliance in an offline network without compromising your security perimeter.
🛑 The Connected SAM Dilemma
When preparing for an Oracle audit, organizations running air-gapped systems are often forced into manual workarounds:
* Database Scripting: DBAs manually run SQL scripts to extract feature usage and core counts.
* Excel Spreadsheets: Compliance managers consolidate hardware configurations and user lists by hand.
* Security Risks: File transfers containing raw database hostnames, IP addresses, and schema structures are copied across boundaries using USB drives or unsecured networks.
This manual process is highly prone to human error, misses critical option triggers, and risks leaking sensitive network topography data.
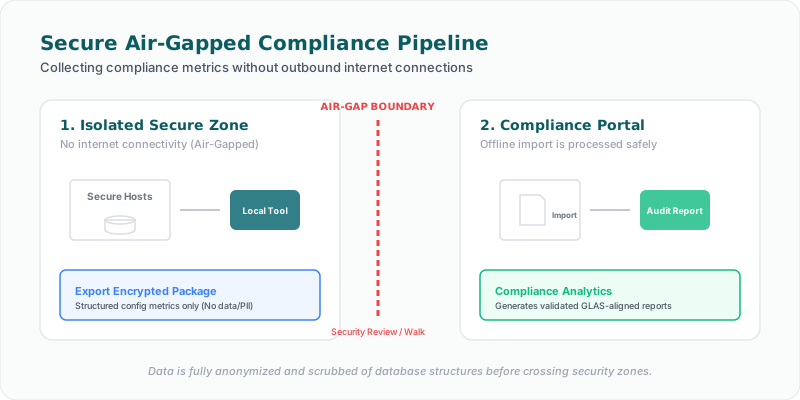
📦 The Solution: Secure Offline Payload Archiving
To automate compliance in a secure zone, your discovery tool must support an offline import/export model.
Rather than streaming data to a cloud endpoint, discovery agents should run locally within the air-gapped network and output structured, secure data packages.
How the Air-Gapped Compliance Pipeline Works:
1. Local Collection: A lightweight database collector runs inside the secure network. It queries local database metadata, physical core allocations, and hypervisor cluster configurations.
2. Pseudonymization: Before the data leaves the server, the collector scrubs the payload, replacing sensitive data (like hostnames, IP addresses, and database names) with secure pseudonyms.
3. Tarball Archiving: The collector compresses the audited metadata into a secure, signed tarball package (.tar.gz).
4. One-Way Export: Using a secure, approved file-transfer gateway (such as a data diode or cross-domain solution), the compliance manager exports the tarball to the non-secure network.
5. Offline Ingestion: The compliance manager uploads the tarball into the SAM dashboard for automated normalization and license optimization mapping.
🚀 Air-Gapped Audits with Licencify
Licencify was built from the ground up to support secure, enterprise-grade database environments. Our local collector includes a native Air-Gapped Ingestion Engine:
* Tarball Exporter: Generates secure, local tarball packages with cryptographically signed payloads to ensure data integrity.
* Local Pseudonymization: Guarantees that no raw network identifiers ever leave your secure environment.
* No Cloud Dependency: The collector runs without any external internet connection or outbound API calls.
* One-Click Upload Portal: The Licencify SaaS platform provides a manual import portal where security teams can upload offline payloads and instantly run license simulations.
Do you run Oracle Databases in secure, air-gapped zones? Schedule a demo with Licencify to see our offline compliance engine in action.
Facing an active Oracle or SQL Server Audit?
Verify database parameters and virtualization host boundaries locally without raw data uploads. Download our secure gateway.